- Squid To Stop DC DDoS.
- Squid On VPS
- Can I Do This With Squid
- How To Test Squid
- Install Squid With Yum
- Squid Error
- Squid And REMOTE_ADDR
- How To Install Squid
- Squid Proxy
- Installing Squid 2.6 On FC4
- SQUID Proxy Config
- Squid + CPanel (Apache)
- Webproxy Trough Squid
- Squid - Shows Clients IP
- Using Squid To Speed Things Up
- IP Address And Squid Proxy Configuration
- Internal Cpanel Port Squid
- Count Network Traffic With Squid Proxy
- Squid Frontend Gives 0 Network Output For Seconds At The Time
- DDoS Protection Providers Vs DDoS Protection Scripts
- Reverse Proxy For Server-A Through Server-B Using Squid
- DDoS?
- UDP DDoS
- Getting Ddos ...
- Bad DDos
- It's A Ddos
- DDos
- DDoS
- DDOS Attack
Showing posts with label explanation. Show all posts
Showing posts with label explanation. Show all posts
Monday, August 8, 2011
DDOS FAQ

Zombie Recruitment: How Attackers Find, Exploit, and Employ You
A crucial element of a DDoS attack is the ability to employ hundreds, thousands, or even millions of infected hosts to do the attacker’s bidding. The reasons are obvious – the end target(s) of the attack will find it more difficult to fend off the malicious traffic, and the attack is less likely to be traced back to the actual perpetrator. These “zombie” hosts are rarely related to the source host of the attack, and are rather infected by other compromised hosts – but can end up causing more damage than the machine that originated the attack in the first place. So you may be wondering – where do zombies come from?
Sunday, August 7, 2011
Belajar VRRP dalam network
Dalam dunia routing kita pasti mengenal static atau default route.
Biasanya static route dan default route dibuat untuk lebih simpel konfigurasi dan memudahkan dalam maintenance.
Biasanya static route dan default route dibuat untuk lebih simpel konfigurasi dan memudahkan dalam maintenance.
Untuk lebih mudah berikut ilustrasi default route :
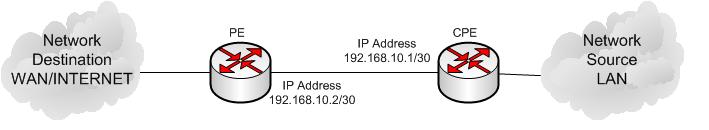
VRRP di Router Juniper
IP adalah protokol jaringan yang digunakan untuk melakukan surfing di internet, download musik, atau game. PC akan memiliki IP address serta default gateway untuk mencapai setiap tujuan yang tidak berada pada subnet lokal. Default gateway dapat didefinisikan oleh pengguna baik secara static atau melalui proses Dynamic Host Configuration Protocol (DHCP). Apapun metode tersebut, default gateway akan digunakan sebagai hop berikutnya untuk rute default yang akan dibuat untuk mencapai tujuan.
Jika default gateway adalah single device dan device tersebut failed, maka PC tidak akan mampu mencapai tujuan di luar subnet lokal. Dalam jaringan fault-tolerant, akan sangat ideal untuk memiliki cadangan gateway device, tanpa harus memodifikasi konfigurasi pada PC, serta dapat di-share dengan beberapa PC di LAN.
VRRP Virtual Router Redundancy Protocol [Mikrotik]
Virtual Router atau VRRP Group merupakan sekumpulan router yang berfungsi untuk kebutuhan redundancy. Secara konseptual VRRP mempunyai satu deviceyang berperan sebagai master dan beberapa router yang akan berfungsi sebagai backup. Pada VRRP, Router Master prioritynya diset 255, sedangkan pada Backup diset antara 1-254, dengan nilai default prioritynya adalah 100 yang masing-masingnya mempunyai sebuah VRID (Virtual Router ID) yang unik.


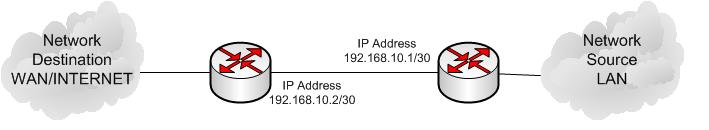
VLAN pada 3Com SuperStack dan Mikrotik Router OS
Tulisan ini menceritakan langkah-langkah setup dan konfigurasi port untuk keperluan VLAN pada switch 3C13700A SuperStack 3 Switch 4200 26-port, pada topologi jaringan sederhana yang menggunakan Mikrotik Router OS pada Router.
Asumsi;
Asumsi;
- Setup awal swicth 3com telah dilakukan sebelumnya
- Sudah dapat melakukan konfigurasi melalui CLI, telnet
Sekilas mengenai VLAN
VLAN berdasarkan definisi adalah logical independent network within a physical network, sebagai ilustrasi yang lebih mudah mungkin serupa tapi tak sama dengan pembagian partisi pada HDD.
Beberapa keuntungan VLAN, disadur dari http://en.wikipedia.org/wiki/VLAN;
- Menambah jumlah broadcast domain tapi mengurangi ukuran masing-masing, yang otomatis menurunkan traffic jaringan dan meningkatkan keamanan.
- Mengurangi kebutuhan untuk membuat subnetwork.
- Mengurangi kebutuhan hardware, jaringan dapat dipisahkan secara logical, tidak harus secara fisik.
- Menambah kendali terhadap berbagai jenis trafiic.
- Membuat beberapa logical swicth di dalam sebuah logical switch.
Layer 2 and security - protecting from attack
Before your access lists or firewall rules comes layer 2(L2). This is the Data link layer where your MAC addressing lives. Why do we need to protect L2…?
Lets hit these guys one at a time:
Man in the middle attack
What is a man in the middle attack? Here’s what wikipedia says about it. In a nutshell I tell the router that I am you, and I tell you that I am the router. What happens is that all your traffic passes through me…while I intercept everything possible about what you are doing. I wait for you to attempt a bank transaction and hand you a bunk site certificate and steal your monies I do this by sending gratuitous ARPs. These are unprovoked ARP announcements. I send ARPs over and over to the router saying I’m you. I then send you ARPs over and over saying that I am the router.
What is a man in the middle attack? Here’s what wikipedia says about it. In a nutshell I tell the router that I am you, and I tell you that I am the router. What happens is that all your traffic passes through me…while I intercept everything possible about what you are doing. I wait for you to attempt a bank transaction and hand you a bunk site certificate and steal your monies
I do this by sending gratuitous ARPs. These are unprovoked ARP announcements. I send ARPs over and over to the router saying I’m you. I then send you ARPs over and over saying that I am the router.
Tuesday, August 2, 2011
Pick Your Poison - ARP, MAC, WiFi
In this paper we will cover the basics on Address Resolution Protocol (ARP), Media Access Control (MAC) Addresses, Wireless (WiFi), and layer 2 communications. I hope to explain how a "Man in the Middle Attack" works. The common name for this is ARP poisoning, MAC poisoning, or Spoofing. Before we can get into how the poisoning works, we need to learn about how the OSI Model works and what happens at layer 2 of the OSI Model. To keep this basic we will only scratch the surface on the OSI model to get the idea of how protocols work and communicate with each other. The OSI (Open Systems Interconnection) Model was developed by the International Standards Organization (ISO)in 1984 in an attempt to provide some standard to the way networking should work. It is a theoretical layered model in which the notion of networking is divided into several layers, each of which defines specific functions and/or features. However this model is only a general guideline for developing usable network interfaces and protocols. Sometimes it may become very difficult to distinguish between each layer as some vendors do not adhere to the model completely. Despite all this the OSI model has earned the honor of being "the model" upon which all good network protocols are based.
Subscribe to:
Posts (Atom)